Answer Summary
Biometrics can reduce identity fraud and strengthen access controls in DME operations, but they introduce privacy, consent, and data-security risks. In 2026, responsible biometric use requires clear purpose limits, explicit consent practices, and alignment with broader compliance and security frameworks.
Introduction
As digital onboarding and portals expand, identity verification becomes harder—and fraud risk grows. Biometrics (fingerprint, face, voice) can help confirm identity quickly, but biometric data is sensitive. If implemented poorly, it creates more risk than it prevents.
Where Biometrics Fit in DME Workflows
Common use cases include:
- secure portal login,
- identity verification during onboarding,
- call center verification via voice (in some implementations),
- access control for staff systems.
Benefits
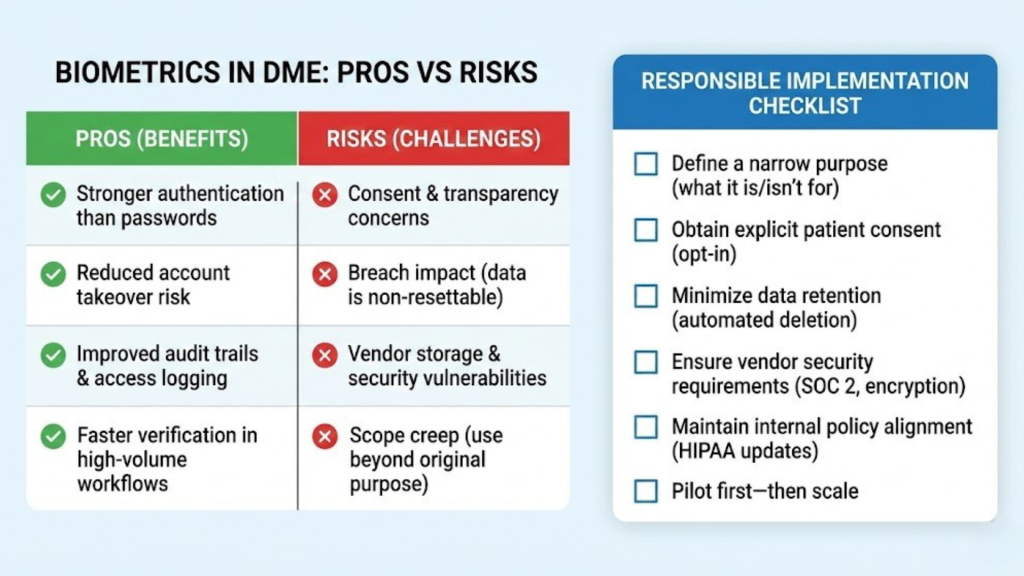
- stronger authentication than passwords,
- reduced account takeover risk,
- improved audit trails and access logging,
- faster verification in high-volume workflows.
Key Risks You Must Plan For
- consent and transparency concerns,
- breach impact (biometric data can’t be “reset” like a password),
- vendor storage and security practices,
- scope creep (biometrics used beyond the original purpose).
A Responsible Implementation Checklist
- define a narrow purpose (what it is for—and what it is not for),
- obtain explicit patient consent,
- minimize data retention,
- ensure vendor security requirements and breach response plans,
- maintain documentation and internal policy alignment,
- pilot first—then scale.
How Wonder Worth Solutions Helps
WWS helps providers evaluate operational security solutions through a compliance-first lens, ensuring new tools strengthen trust and reduce risk.
Conclusion
Biometrics can be a powerful security upgrade—but only when purpose-limited, consent-led, and governed by strong security discipline.